AI solutions we’ve built Example build
Security Program
Maturity, vulnerabilities, findings and audit evidence in one place – ranked by real exposure, with every finding chased to done and the evidence collected as you go.
The problem
- Scanners report thousands of vulnerabilities, all marked urgent
- Audit findings slip past their due dates with no one chasing
- Every audit means weeks of collecting screenshots by hand
Example build – typical timeline
DiscoveryDays 1–8requirements, architecture, data and access
Build7 days3 proof of concept + 4 back end
In useDay 15working prototype
Production-readyDay 28refined with users, tested, rolled out
Working days from kickoff. Discovery is typical for a new client; from in use to production-ready, we refine it with your users every week. What it runs on and costs to run
Take the tour click a number or use the arrow keys
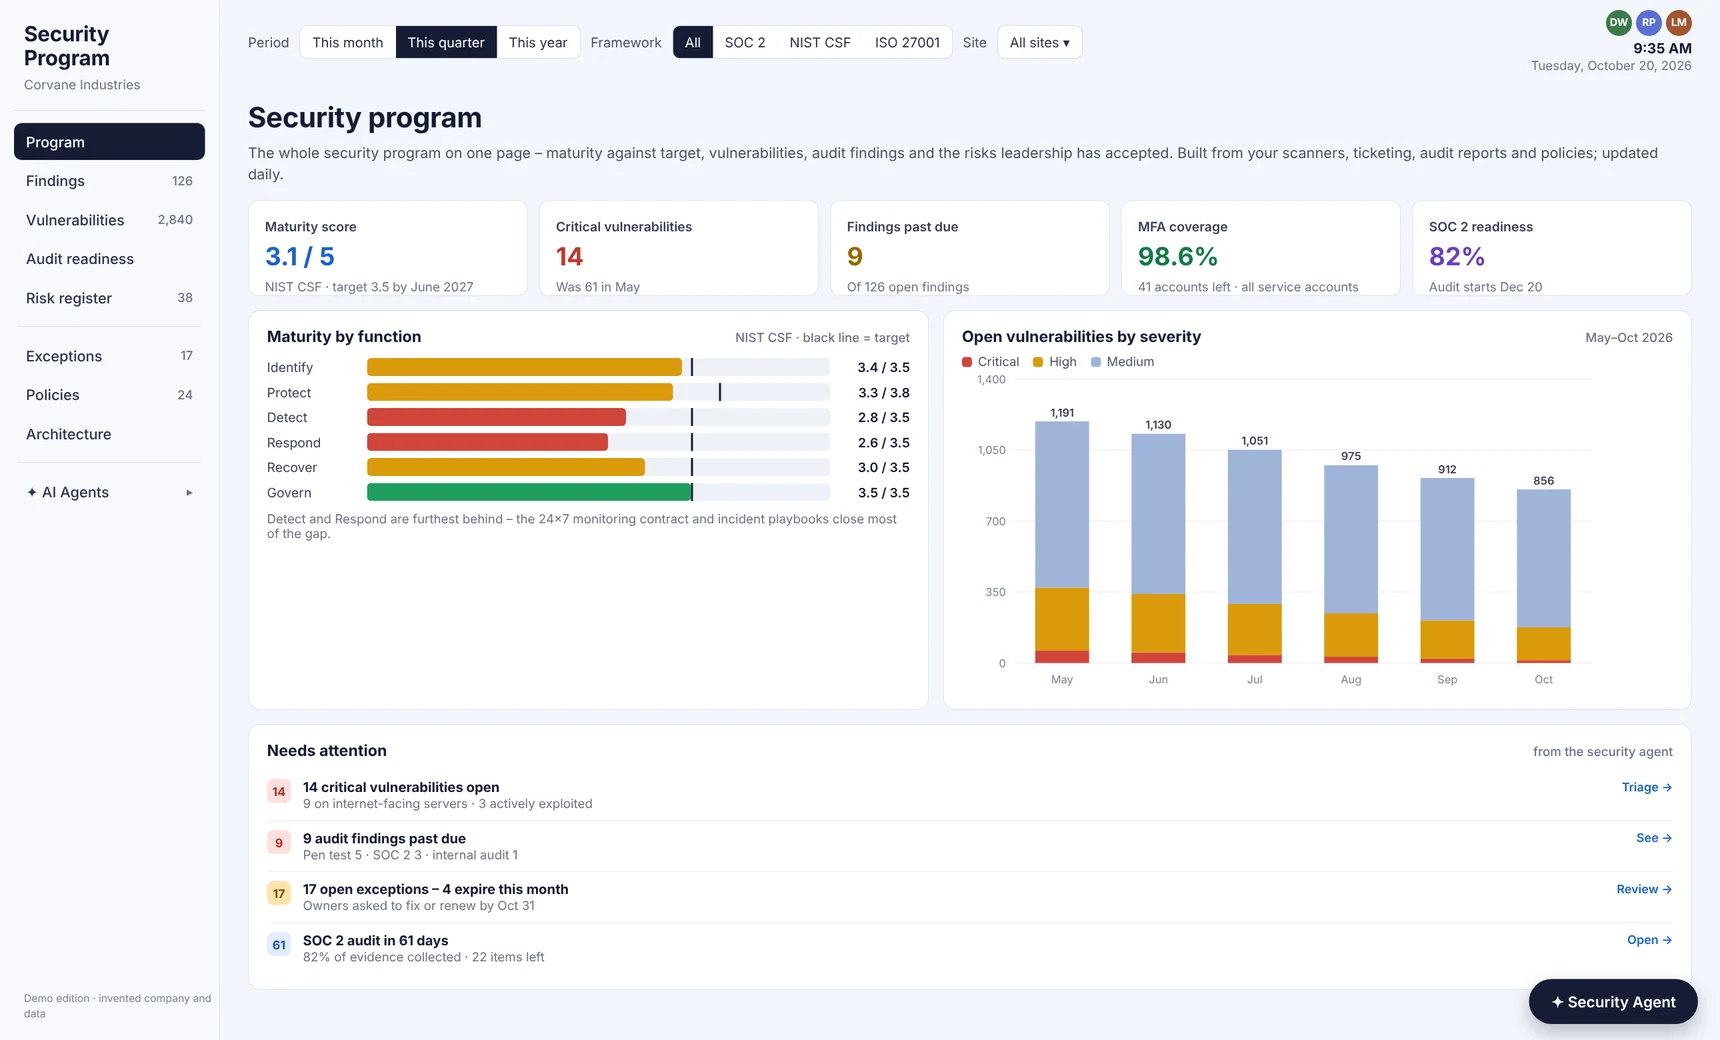
The whole security program on one page
Maturity against target, vulnerabilities, findings past due and what needs attention
Watch it in about a minute
Built into your architecture
Security ProgramRuns inside your environment – read-only in your security tools
Your vulnerability scannersServers, laptops, cloud and network
Your pen tests and auditsReports turned into findings
Your security toolsIdentity, endpoint and monitoring coverage
Your ITSM toolFix work as tickets and changes